
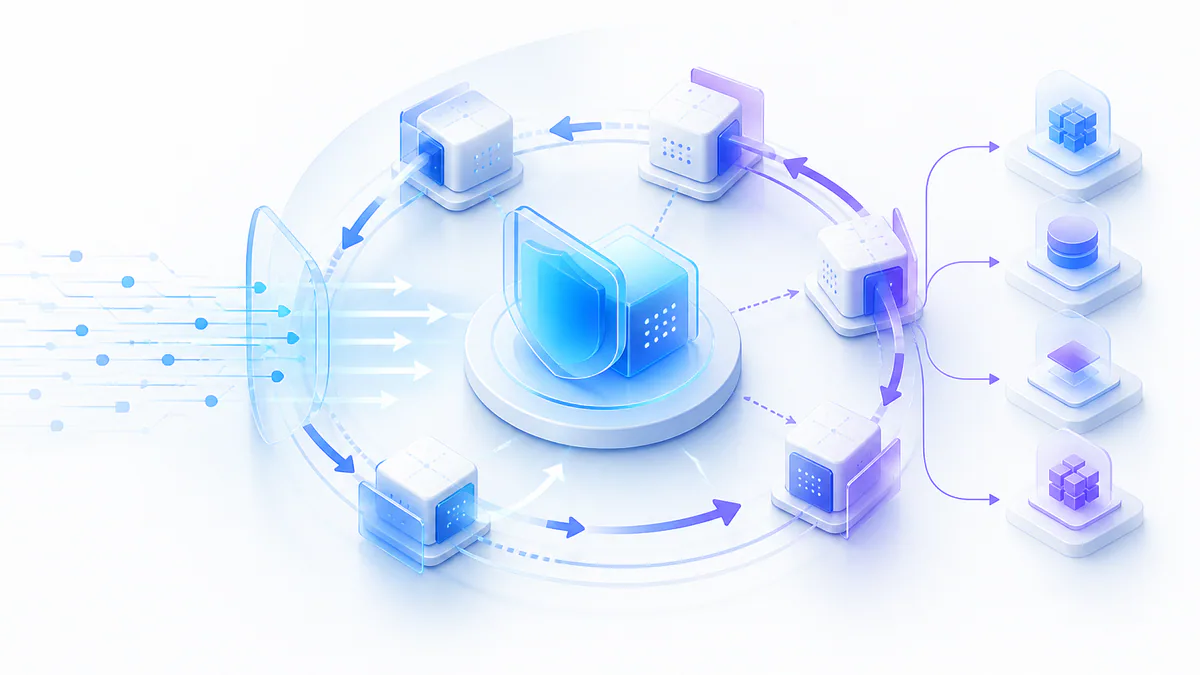
A reverse rotating proxy usually refers to a backconnect-style proxy gateway that automatically routes your outgoing requests through changing proxy IP addresses. You connect to one host and port while the gateway selects the exit behind it. Despite the name, this is different from a traditional reverse proxy, which receives incoming traffic on behalf of backend servers.
| Common meaning | A backconnect-style rotating proxy gateway |
|---|---|
| Client connection | One stable gateway hostname and port |
| Exit IP | Selected from a larger proxy pool and allowed to rotate |
| Rotation modes | Per request, timed, session-based, or sticky |
| Traffic role | Primarily outbound traffic on behalf of the client |
| Common IP types | Datacenter, residential, mobile, and ISP |
| Traditional reverse proxy? | No — the terms describe different architectures |
- “Reverse rotating proxy” is common commercial proxy terminology, but it is not the same thing as a traditional reverse proxy used in web-server infrastructure.
- In most proxy-service contexts, the phrase describes a client-facing gateway that routes outbound requests through a rotating pool of exit proxy IPs.
- That architecture overlaps heavily with what the industry more clearly calls a backconnect proxy.
- The word “rotating” describes changing exit IPs; the gateway can rotate every request, after a time interval, or preserve one exit temporarily through a sticky session.
- The underlying exits can be datacenter, residential, mobile, or ISP addresses. “Reverse rotating” describes how the pool is accessed and managed, not the origin of the IPs.
What Is a Reverse Rotating Proxy?
A reverse rotating proxy usually refers to a proxy gateway that accepts a connection from your application and routes outbound requests through a pool of changing proxy IP addresses. You keep one client-facing hostname and port, while the provider manages the exit IPs behind that endpoint.
Despite the name, this setup is different from a traditional reverse proxy. A conventional reverse proxy normally sits in front of one or more backend web servers and receives incoming requests on their behalf. A reverse rotating proxy service, by contrast, is normally used by a client that wants its own outgoing traffic to leave through different proxy IPs.
The most useful mental model is therefore: one gateway in front, many possible exit proxies behind it. The gateway can authenticate the account, enforce connection limits, select a proxy pool, preserve or rotate a session, avoid unhealthy exits, and forward traffic using HTTP(S) or SOCKS5.
Terminology note
The phrase “reverse rotating proxy” is used inconsistently. In commercial proxy services it commonly describes the same basic single-gateway rotating architecture that is more clearly called a backconnect proxy. Read our Backconnect Proxy guide
Why the Name “Reverse Rotating Proxy” Is Confusing
Networking terminology already has a specific meaning for “reverse proxy.” A reverse proxy represents servers: users send traffic to the reverse proxy, and it decides which backend application or server should receive that traffic. That is the architecture used for load balancing, TLS termination, caching, web application firewalls, and hiding backend server topology.
Rotating proxy providers use the word “reverse” differently in some product names. They are usually describing a gateway that hides a changing pool of outbound proxies behind one access point. Because the client is still using the service to reach external destinations, the traffic pattern behaves much more like a forward-proxy or backconnect system than a conventional reverse proxy.
What Proxy Providers Usually Mean by the Term
When a provider sells reverse rotating proxies, the product usually gives the customer a stable endpoint such as gateway.example.com:8000. The customer authenticates once against that gateway, while the service maps new requests or sessions to different backend proxy IPs.
The exact implementation can vary. Some services rotate on each new request, some assign one exit for a time window, and some allow the user to create a sticky session. The core idea is not a special protocol; it is provider-managed routing between one client endpoint and a larger proxy pool.
The Single-Gateway Model
Without a gateway, a client may need to store hundreds or thousands of individual proxy endpoints and decide which one to use for each task. With a reverse rotating gateway, the application can keep one configuration while the backend pool changes independently.
This abstraction is particularly useful when many workers share the same proxy service. Instead of distributing updated proxy lists to every worker, the provider can add, remove, cool down, or replace exits behind the gateway.
How Do Reverse Rotating Proxies Work?
A reverse rotating proxy has two distinct layers: the front-facing gateway and the backend proxy pool. Your application knows the gateway. The destination website sees the selected exit proxy. The rotation service connects those two layers.
A well-designed gateway does more than choose a random IP. Depending on the service, selection logic can consider protocol, requested geography, session identifiers, pool availability, active connections, recent failures, health status, and account limits before assigning an exit.
Step 1 — Connect to the Proxy Gateway
The client starts by opening a connection to a configured hostname and port. This endpoint can stay the same even while the provider changes the backend servers or adds more IP addresses to the pool.
Step 2 — Authenticate the Connection
Authentication is commonly performed with a username and password or by allowing traffic from a whitelisted source IP. Some providers encode routing options such as country or session identifiers into the username, while others expose separate ports or API settings.
Step 3 — Select an Exit Proxy
The gateway chooses an exit that matches the rules for the current request. In per-request mode, a new selection may occur frequently. In sticky mode, the system tries to map related requests to the same exit for the configured session duration.
Step 4 — Forward the Request
The selected proxy establishes the upstream connection and sends the request to the destination. The destination normally sees the exit proxy IP rather than the customer’s direct public IP.
Step 5 — Rotate or Preserve the Exit IP
When the next request arrives, the gateway applies the rotation policy again. It can preserve the existing mapping, select another exit, or fail over if the previous backend has become unhealthy.
Reverse Rotating Proxy Architecture
The architecture becomes easier to understand when the gateway and exit nodes are treated as separate components. The gateway is the control point your application connects to. The proxy pool is the set of network identities that can actually reach the destination.
Because those roles are separated, the provider can change the backend network without forcing every customer to reconfigure its application. The gateway can also centralize authentication, concurrency enforcement, bandwidth accounting, session mapping, retry logic, health checks, and protocol handling.
Typical gateway responsibilities
- Authenticate accounts through username/password or IP authorization.
- Apply per-account and per-source concurrent connection limits.
- Select an eligible proxy pool and backend exit.
- Respect per-request, timed, or sticky-session rotation rules.
- Avoid or cool down failing backend proxies.
- Forward HTTP, HTTPS tunnel, or SOCKS5 connections.
- Track bandwidth, connections, requests, failures, and operational health.
Reverse Rotating Proxy vs. Reverse Proxy
A reverse rotating proxy and a traditional reverse proxy solve different problems. The traditional reverse proxy protects and represents backend servers. The reverse rotating proxy service represents a client that wants outgoing requests to use changing proxy exits.
This difference matters because the word “reverse” can otherwise lead to the wrong mental model. Nginx, HAProxy, Caddy, cloud load balancers, and CDNs are common examples of technologies that can act as true reverse proxies. A rotating proxy gateway used for scraping, monitoring, or browser automation is normally a client-side access service instead.
Outbound traffic is routed on behalf of the client through changing exit proxies.
Incoming traffic is received and routed on behalf of the server-side application.
| Area | Reverse Rotating Proxy | Traditional Reverse Proxy |
|---|---|---|
| Represents | The client making outbound requests | The backend server/application |
| Traffic pattern | Client → proxy gateway → exit proxy → website | Internet user → reverse proxy → backend server |
| Main purpose | Change or manage outbound network identities | Load balance, secure, cache, or hide backend servers |
| IP rotation | Usually a core feature | Not inherently part of the architecture |
| Proxy pool | Pool of outbound exit IPs | Pool of backend/upstream servers |
| Typical users | Scrapers, monitors, automation systems, testing tools | Websites, APIs, application infrastructure |
| Closest common proxy term | Backconnect / rotating forward proxy | Reverse proxy |
What Is a Traditional Reverse Proxy?
A traditional reverse proxy accepts requests that are intended for a website or service and forwards them to one or more backend servers. The visitor may never know which backend handled the request. This makes the reverse proxy a useful control point for TLS, routing, caching, rate limiting, application security, and load balancing.
What Is a Forward Proxy?
A forward proxy acts on behalf of the client. The client intentionally sends its outbound traffic to the proxy, and the proxy connects to the destination on the client’s behalf. Commercial datacenter, residential, SOCKS5, and rotating proxies normally operate in this general direction.
Why the Two Should Not Be Confused
Calling a rotating gateway a “reverse proxy” without context can be misleading because the direction and protected party are different. For SEO and product terminology, “reverse rotating proxy” is still useful because people search for it. For technical explanation, however, it is better to explicitly state that the service is usually a rotating backconnect or forward-proxy gateway.
Reverse Rotating Proxies vs. Backconnect Proxies
In commercial proxy terminology, reverse rotating proxies and backconnect proxies usually describe the same basic delivery model: the user connects to one gateway while the provider chooses and rotates outbound proxy exits behind that gateway.
“Backconnect proxy” is generally the clearer term because it describes the gateway-to-pool architecture without colliding with the established networking meaning of reverse proxy. If a service offers one stable endpoint, automatic backend selection, optional sticky sessions, and a rotating pool of exits, it is reasonable to think of it as a backconnect system regardless of the marketing label.
Deep dive
For the full gateway architecture, sticky-session, provider-selection, and proxy-type explanation, see What Are Backconnect Proxies?
| Question | Reverse Rotating Proxy | Backconnect Proxy |
|---|---|---|
| Usually one client-facing gateway? | Yes | Yes |
| Backend proxy pool? | Yes | Yes |
| Automatic exit selection? | Usually | Usually |
| Per-request rotation? | Common | Common |
| Sticky sessions? | Often supported | Often supported |
| Technically clearer term? | More ambiguous | Usually clearer |
Reverse Rotating Proxies vs. Rotating Proxies
“Rotating proxy” describes behavior: the exit IP changes according to a rule. “Reverse rotating proxy” usually adds an architectural assumption: one gateway is performing that rotation for the client.
A rotating setup does not require a gateway. A Python script can download a list of 1,000 proxies and choose a different one for each request. That is still proxy rotation, but the client owns the rotation logic. With a reverse rotating or backconnect service, the gateway handles the selection instead.
Related guide
For a broader explanation of IP-changing behavior without the gateway terminology, read What Are Rotating Proxies?
| Area | Reverse Rotating Proxy | Rotating Proxy |
|---|---|---|
| Describes | Gateway-based rotating service | IP-changing behavior |
| One stable endpoint | Usually | Not required |
| Who chooses the exit? | Usually the provider gateway | Provider or client |
| Manual proxy list possible? | Usually unnecessary | Yes |
| Sticky sessions possible? | Yes | Yes |
| Best mental model | How rotation is delivered | What the IP does |
How IP Rotation Works
The gateway needs a rule for deciding when the network identity should change. There is no single rotation schedule that is best for every workload. Stateless requests can tolerate aggressive rotation, while multi-step sessions usually need continuity.
Providers can expose rotation through different interfaces, but the three most useful concepts are per-request rotation, time-based rotation, and sticky sessions.
Per-Request Rotation
Per-request rotation allows a different exit to be selected for each new request or connection. A simplified pattern could be Request 1 → IP A, Request 2 → IP B, Request 3 → IP C.
This is useful for independent public-data requests where each transaction stands alone. It is less suitable when the destination expects several requests to belong to the same browser or authenticated session.
Time-Based Rotation
Time-based rotation keeps a mapping for a defined period, such as one, five, or ten minutes, before allowing another exit to be selected. This can reduce unnecessary identity changes while still distributing longer jobs across the proxy pool.
Sticky Sessions
A sticky session attempts to preserve one exit IP for a sequence of related requests. Services can implement this with a session identifier, a dedicated port, a username parameter, or internal state tied to the client connection.
Sticky does not necessarily mean permanent. The exit can still disappear because of a backend failure, pool change, provider timeout, or maximum session duration. Applications should therefore handle the possibility that a sticky exit eventually changes.
Sticky sessions make sense when
- Several requests need to share cookies or a login session.
- A multi-step workflow should keep a consistent temporary network identity.
- Per-request rotation would make the destination see unrealistic IP changes.
Types of Reverse Rotating Proxies
The gateway architecture does not determine what kind of IP address sits behind it. A reverse rotating service can route traffic through datacenter, residential, mobile, or ISP proxy pools.
The choice affects speed, price, location coverage, network identity, session stability, and how easily a destination can recognize the network as hosting infrastructure.
| Proxy Type | Typical Strengths | Typical Tradeoffs | Common Fit |
|---|---|---|---|
| Datacenter | High throughput, low latency, predictable infrastructure, lower cost | Clearly associated with hosting/datacenter networks | High-volume automation, scraping, monitoring, testing |
| Residential | Consumer ISP address space and broad geo coverage | Higher cost and commonly bandwidth-priced | Geo-sensitive public-web collection and testing |
| Mobile | Mobile carrier IP space and carrier-network characteristics | High cost and more limited capacity | Mobile-specific validation and research |
| ISP | Stable hosted infrastructure with ISP-associated address space in many products | Availability and definitions vary by provider | Longer-lived sessions that benefit from stable exits |
Datacenter Reverse Rotating Proxies
Datacenter reverse rotating proxies use backend IPs hosted on servers and datacenter networks. They are a strong fit when speed, concurrency, predictable routing, and cost efficiency are more important than appearing as a consumer ISP connection.
For large public-data pipelines, price monitoring, SEO checks, and automation infrastructure, datacenter exits can provide high throughput without requiring the client to manually manage thousands of addresses.
Residential Reverse Rotating Proxies
Residential pools use IP addresses associated with consumer internet providers. They are frequently sold through a rotating gateway because the underlying pool can be large and dynamic. The customer connects to one endpoint while the provider handles available residential exits.
Mobile Reverse Rotating Proxies
Mobile proxy pools route through carrier-associated addresses. They can also be hidden behind a rotating gateway, but they are usually more expensive and capacity-constrained than datacenter pools.
ISP Reverse Rotating Proxies
ISP proxy products combine hosted proxy infrastructure with address space associated with internet service providers. Terminology varies between vendors, so buyers should confirm whether the product is static, rotating, dedicated, or shared rather than relying on the category name alone.
Benefits of Reverse Rotating Proxies
The main advantage is operational simplicity. The client can treat the service as one stable access layer while the provider manages the changing proxy fleet behind it.
This becomes increasingly valuable as the pool or number of application workers grows. Centralized gateway logic can remove a large amount of duplicate rotation and health-management code from individual clients.
One Gateway Instead of Thousands of IPs
A scraper can continue using the same gateway even if the provider adds or replaces large numbers of backend proxies. This separates application configuration from proxy inventory.
Automatic IP Rotation
The service can automatically distribute requests across many exits according to a defined rotation policy, reducing the need for custom proxy-selection code in every application.
Easier Scaling
Multiple workers can share the same gateway format. Scaling the application from a few threads to a larger distributed workload does not necessarily require distributing a new proxy list to every worker.
Proxy Health and Failover
A gateway can stop assigning traffic to exits that repeatedly fail and reintroduce them after recovery. This does not eliminate upstream errors, but it can prevent every client from independently discovering the same unhealthy proxy.
High Concurrency
Datacenter-oriented rotating gateways can be designed for many simultaneous connections. The practical limit still depends on the purchased plan, gateway capacity, backend capacity, destination behavior, and application timeouts.
Geographic Distribution
Providers can expose different country or region pools through credentials, ports, or separate gateway names. The client chooses the required pool without needing to know every individual IP inside it.
Limitations of Reverse Rotating Proxies
A rotating gateway solves proxy management problems, not every problem involved in reliable web automation. It can simplify IP selection and distribution, but the destination can still evaluate many other signals.
A useful provider comparison should therefore include the limitations as well as the benefits.
Less Direct Control Over Individual IPs
The gateway decides which backend exit is available under the current rules. If your application needs to select a specific IP address by exact identity, an individual proxy list or dedicated static proxy may provide better control.
IP Rotation Can Break Sessions
Changing IP addresses during a login, cart, checkout, or multi-step browser flow can look inconsistent and may invalidate state. Sticky-session support is important whenever requests are related.
Shared IP Reputation
In shared pools, an exit can have history from other customers. Rotation cannot guarantee that every IP has identical reputation, reachability, or success against every destination.
The Gateway Adds Another Network Layer
Every proxy adds network distance and processing. Gateway design, backend distance, DNS resolution, destination latency, TLS setup, and congestion can all affect response time.
Rotation Does Not Solve Browser Fingerprinting
A new IP address does not automatically change cookies, TLS characteristics, browser fingerprints, request headers, account history, navigation patterns, or request timing. Websites can combine several signals, so IP rotation should not be treated as a universal method for avoiding detection.
What Are Reverse Rotating Proxies Used For?
Reverse rotating proxies are most useful when an application needs many outbound requests but should not be permanently tied to one proxy IP. The gateway reduces proxy-management overhead while rotation distributes traffic across a broader network.
They should be used in accordance with the destination’s terms, access rules, applicable law, and responsible request-rate practices.
Web Scraping and Public Data Collection
Large crawlers can route independent public-data requests through a rotating pool without loading a large proxy list into each worker. Sticky sessions can be used for workflows that require several related page requests.
Price Monitoring
E-commerce monitoring systems can distribute scheduled product and price checks across many exits, especially when collecting public information across regions or large catalogs.
SEO and SERP Monitoring
Rank-tracking systems generate repeated search and page requests. A gateway can make it easier to distribute those requests across proxy exits and regional pools.
Ad Verification
Verification workflows can use location-specific proxy pools to inspect public campaign and landing-page behavior from different network locations.
Browser Automation and QA
Automated browsers can use rotating proxies for localization checks, public-page validation, testing, and workflows where network identity needs to vary between sessions.
Market and Content Monitoring
News, review, competitor, marketplace, and public-content monitoring pipelines can centralize proxy routing through one gateway instead of maintaining separate proxy lists in each service.
When Should You Not Use Reverse Rotating Proxies?
A rotating gateway is not automatically the best proxy type. In some workflows, stability and precise control matter more than rotation.
Consider a static or dedicated setup instead when
- A third party must permanently allowlist one exact source IP.
- A workflow depends on one long-lived IP identity and the provider cannot guarantee an adequate sticky session.
- You need direct control over which individual IP serves each task.
- The workload is tiny and client-side rotation of a few proxies is simpler than using a gateway service.
- Ultra-low latency is more important than the operational benefits of a gateway and proxy hop.
- The application is server infrastructure that actually needs a true reverse proxy such as Nginx, HAProxy, Caddy, a CDN, or a cloud load balancer.
How to Use a Reverse Rotating Proxy
From the application’s perspective, a reverse rotating proxy is configured like a normal authenticated proxy endpoint. The rotation happens behind the endpoint, so the client generally does not need to know which exit was selected.
Exact formats differ by provider. The examples below use placeholder credentials and domains; replace them with the values from your proxy service.
ProxyTitan product
ProxyTitan provides a commercial backconnect gateway for rotating datacenter proxy workflows. View Backconnect Proxies
Gateway Format
The most common formats are host:port for IP-authenticated access and username:password@host:port for credential-based access.
gateway.example.com:8000username:[email protected]:8000HTTP / HTTPS With cURL
For HTTP proxy access, cURL can send the request through the gateway. HTTPS destinations normally use an HTTP CONNECT tunnel when the proxy supports it.
curl -x "http://username:[email protected]:8000" \
  "https://api.ipify.org?format=json"
SOCKS5 With cURL
If the service exposes SOCKS5, use the SOCKS5 gateway and credentials supplied by the provider. The socks5h scheme also resolves the destination hostname through the proxy.
curl --proxy "socks5h://username:[email protected]:1080" \
  "https://api.ipify.org?format=json"
Python Example
Python requests can use the same gateway for multiple requests. If the proxy is configured for per-request rotation, repeated calls can return different public exit IPs even though the proxy URL in the application never changes.
import requests

proxy = "http://username:[email protected]:8000"

proxies = {
    "http": proxy,
    "https": proxy,
}

for i in range(5):
    response = requests.get(
        "https://api.ipify.org?format=json",
        proxies=proxies,
        timeout=15,
    )
    response.raise_for_status()
    print(i + 1, response.json())
Testing Reverse Proxy Rotation in Practice
A useful proxy article should show how to verify rotation instead of merely claiming that it happens. You can test a gateway by sending repeated requests to an IP-echo endpoint and recording the exit address, response time, status, and failures.
Do not publish invented performance numbers. Run the test against the actual production service and publish the date, protocol, request count, rotation mode, concurrency, and measurement method so readers can understand what the result represents.
Test Methodology
Start with sequential requests because they make the rotation pattern easy to inspect. Then repeat with realistic concurrency if you want to evaluate throughput or connection behavior. For sticky sessions, run several requests under the same session identifier and verify that the exit remains stable for the intended window.
Record at least
- Total requests sent.
- Successful and failed requests.
- Unique exit IP count.
- Rotation mode and session settings.
- Average, median, and optionally P95 latency.
- Protocol used: HTTP(S) or SOCKS5.
- Test date and target endpoint.
Python Rotation Test
The following example records the exit IP and elapsed time for each request. Replace the placeholder gateway with your own proxy credentials.
import time
import requests

proxy = "http://username:[email protected]:8000"
proxies = {"http": proxy, "https": proxy}

observed = []

for i in range(20):
    started = time.perf_counter()

    try:
        response = requests.get(
            "https://api.ipify.org?format=json",
            proxies=proxies,
            timeout=15,
        )
        response.raise_for_status()

        elapsed_ms = (time.perf_counter() - started) * 1000
        exit_ip = response.json()["ip"]
        observed.append(exit_ip)

        print(
            f"{i + 1:02d}  "
            f"ip={exit_ip:<15}  "
            f"latency={elapsed_ms:.0f}ms"
        )

    except requests.RequestException as exc:
        print(f"{i + 1:02d}  error={exc}")

print("successful:", len(observed))
print("unique IPs:", len(set(observed)))
Add Real ProxyTitan Results
For the published ProxyTitan article, replace this guidance with a real results table once you have run the benchmark. A strong first-party section could show request count, unique exits, success rate, median latency, P95 latency, protocol, and rotation mode.
First-party measurements give the page something that generic definition articles cannot reproduce. They also make future updates meaningful because you can repeat the same methodology after infrastructure changes.
How to Choose a Reverse Rotating Proxy Provider
The keyword “reverse rotating proxy” tells you very little about the quality of the underlying service. The provider still needs enough healthy proxy capacity, reliable gateways, useful session controls, suitable locations, and transparent limits for your workload.
Evaluate the service against the actual application rather than selecting on pool-size marketing alone.
Questions worth asking before buying
- Does the provider clearly state whether the product is datacenter, residential, mobile, or ISP-based?
- Can you choose between per-request rotation and sticky sessions?
- What happens when a backend proxy fails during an active session?
- How many simultaneous connections does the plan allow?
- Are HTTP(S) and SOCKS5 both available if your applications need them?
- Can the service be tested before committing to a larger plan?
| Area | What to Check |
|---|---|
| Gateway reliability | Uptime, connection stability, timeout behavior, failover, and maintenance history |
| Rotation modes | Per-request, timed, sticky, and session identifier controls |
| Proxy pool | Underlying IP type, usable capacity, countries, network diversity, and replacement policy |
| Concurrency | Per-account thread/connection limits and how limits are enforced |
| Protocols | HTTP, HTTPS CONNECT, SOCKS5, DNS behavior, IPv4/IPv6 where relevant |
| Authentication | Username/password, IP allowlisting, credential management, and security |
| Bandwidth | Included traffic, unlimited/fair-use rules, throughput limits, and overage pricing |
| Observability | Usage statistics, error visibility, documentation, status information, and support |
| Pricing | Cost relative to usable success rate, bandwidth, concurrency, and operational effort |
Conclusion: What Does “Reverse Rotating Proxy” Really Mean?
In the commercial proxy market, a reverse rotating proxy usually means a single gateway that routes a client’s outbound traffic through a rotating proxy pool. The gateway stays simple for the application while the provider manages exit selection, rotation, health, sessions, and backend changes.
The phrase should not be confused with a traditional reverse proxy used to route incoming traffic to backend web servers. Technically, the commercial service is much closer to a rotating forward proxy or backconnect proxy.
If your goal is automatic datacenter IP rotation through one stable endpoint, the backconnect architecture is the relevant product model. If your goal is to protect or load-balance your own web servers, you are looking for a true reverse proxy instead.
Next step
For ProxyTitan’s commercial rotating gateway service, see Backconnect Proxies
Reverse Rotating Proxy FAQ
These short answers address the terminology and implementation questions that most often appear when comparing reverse rotating proxies, backconnect proxies, rotating proxies, static proxies, and traditional reverse proxies.
Need a single gateway with automatic datacenter IP rotation?
ProxyTitan backconnect proxies provide the commercial gateway architecture commonly described by the term reverse rotating proxy: one endpoint in front of a managed rotating datacenter pool.